Shaquille O’Neal’s Cybersecurity Wake-Up Call Puts Consumer Privacy in Focus
After scammers targeted him, Shaquille O’Neal says he’s paying closer attention to digital security and helping explain its everyday risks.
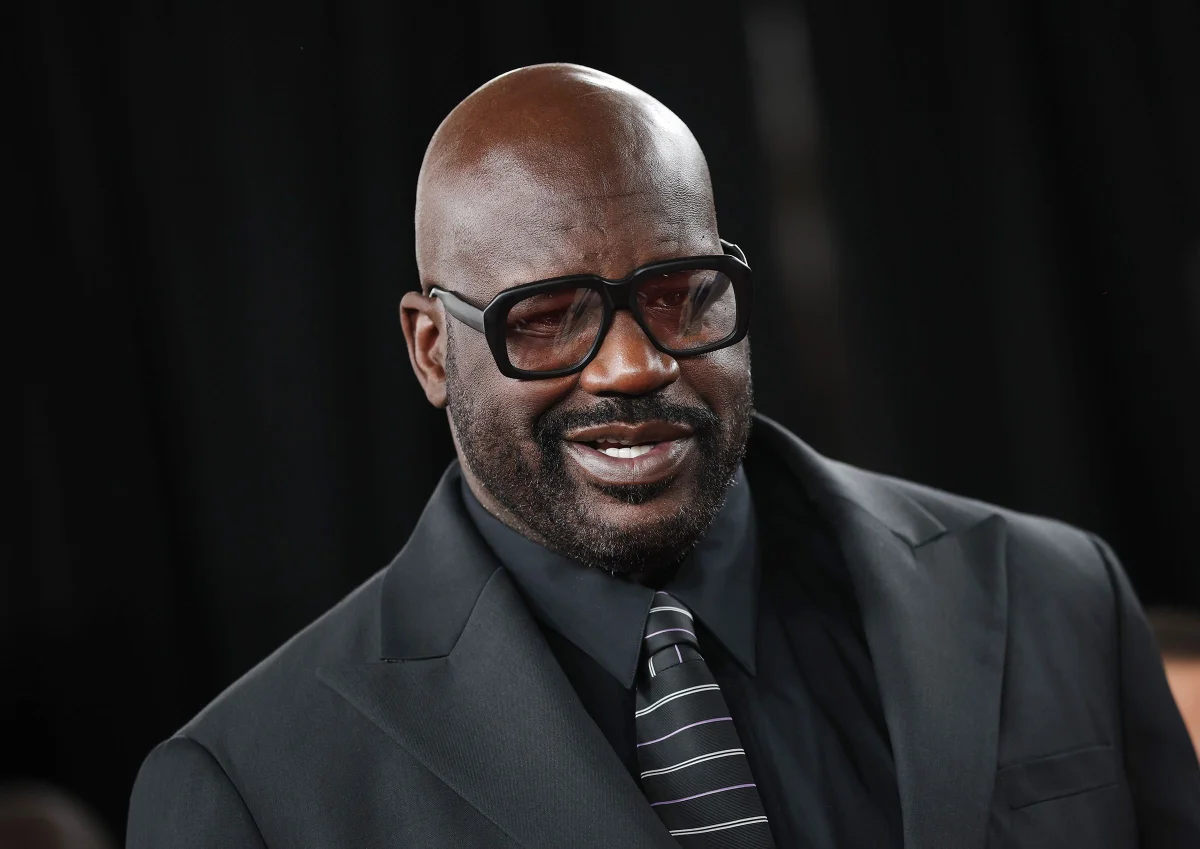
Shaquille O’Neal’s experience with scammers gave him a personal reason to pay closer attention to cybersecurity. Now, as a NordVPN brand ambassador, he’s using that experience to encourage people to think about who can access their information and how they respond when something goes wrong.
At a promotional event in Times Square on Wednesday, O’Neal described a scam involving people who said they were helping with a home purchase. The encounter prompted him to learn more about digital security and personal privacy. He also said he had experienced what he called a minor hack, and initially wasn’t sure how to handle it.
“I was hacked for the first time, not a bad hack, and I didn't know what to do,” he told reporters. The incident changed his assumptions: “I would think nothing like that could ever happen to me, but it could happen to anybody.”
From a personal incident to a broader message
O’Neal framed the issue in terms of control over personal information. He joked about a video of himself and former basketball player Charles Barkley, then made the point he wanted the audience to remember: “But everybody needs to have control of their own information.” The joke is light, but the concern behind it is familiar: people can have private details, accounts, and communications exposed in ways they didn’t expect.
His public profile gives him reasons to think about added precautions. O’Neal said he considers the safety of himself and his loved ones, while trying not to let that concern dominate his life. “Yes, I think about it all the time, but I don't let it consume me, because if you let it consume you you can go crazy,” he said. He added that people need to be ready to respond if a problem occurs.
That emphasis on response matters because a security incident can leave people unsure where to start. O’Neal’s account doesn’t describe technical details about the hack, how it happened, or what steps resolved it. It does show how an unexpected encounter can push someone to seek information and reconsider everyday habits, even when they had assumed they were unlikely to be targeted.
Security tools have limits
O’Neal’s work with NordVPN is presented as an effort to make security information more accessible. The company is best known for its VPN, and also offers antivirus, threat detection, and products intended to help consumers identify scams. Those tools address different parts of online risk; the account doesn’t claim that any single product can prevent every kind of fraud or intrusion.
That distinction is relevant to a finding shared by NordVPN chief technology officer Marijus Briedis. He said he was surprised by a company survey reporting that 73 percent of Americans overestimate what traditional antivirus software can do. In the survey, respondents believed antivirus could protect them against threats ranging from identity theft to online tracking. The figure reflects the company’s own research, as described at the event.
Antivirus can be one part of a security setup, but Briedis’s remarks point to a mismatch between what people expect from a product and the range of risks they face. Identity theft and tracking, for example, aren’t interchangeable problems. A tool designed to detect malicious software shouldn’t automatically be assumed to address every way personal information can be collected, misused, or exposed.
Education is part of the product problem
Briedis said NordVPN is focusing on education because people’s decisions are part of the security challenge. “The weakest link is between the computer and the chair, and I've been thinking so much about how to solve that problem,” he said. He described finding an effective way to teach people as a difficult question, adding that it continues to occupy his thoughts.
That framing puts a practical limit on the value of security software: products can provide protections, but people still need to recognize suspicious requests, understand what a tool covers, and know what to do when an incident happens. O’Neal’s story makes that gap concrete. He said he didn’t know how to react when he was hacked, then began learning more about digital defense.
O’Neal is also a technology investor who backed AI early, according to Forbes. But his message here is less about technology investment than everyday preparedness: security problems can reach people who don’t consider themselves likely targets, and understanding a tool’s limits is part of using it well.
For consumers, the clearest takeaway is to treat privacy and security as ongoing habits, not as a one-time software purchase. O’Neal’s experience offers a reason to pay attention; Briedis’s comments underline the work still needed to help people turn that attention into informed choices.


